Custom deployments
Use a root HTTPS installation on port 443 with a device-trusted certificate and the mobile-connect update. An anonymous GET to index.php?r=mobile.capabilities must return application/json with product proofbetter and mobile_api 1, without redirecting. Back up and merge the new route into the existing entry point before authenticated routing; no database migration is required. Preserve native-client purchase suppression and the compact login layout. ONBOARDING-30006.md documents that compatibility endpoint; the newer MOBILE-REVIEW-30007.md documents the review patch.
In the app, choose Settings → Connect to your server, enter the administrator-supplied address, Check server, then confirm Sign out and connect. Switching clears old local sessions, cache, history and device unlock before selecting the new exact origin. It does not delete server accounts. Subdirectories, alternate ports and IPv6 literals are not supported. Never relax TLS. Local or VPN hosts must already be reachable; allow local-network permission if prompted and select the Android 17+ local-network option for LAN hosts. No scanning or VPN setup is performed.
Mobile markup and recording
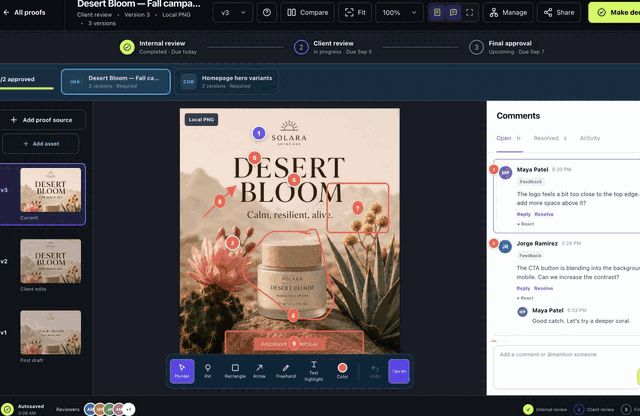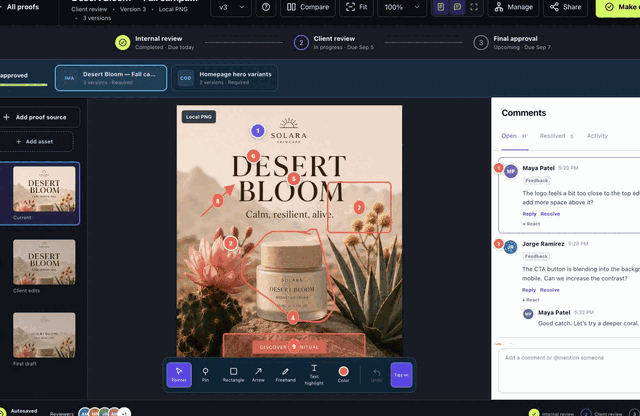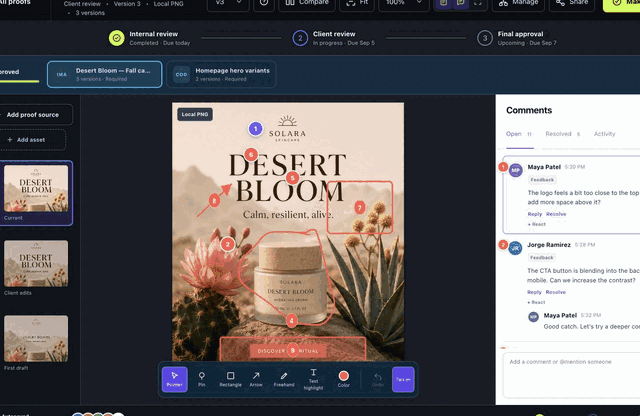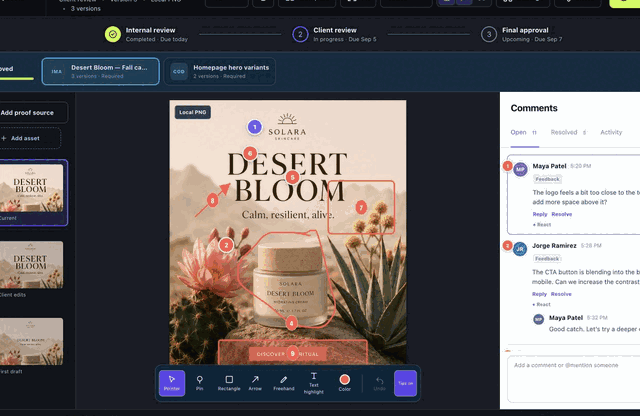
Deploy the matching index.php, app/views.php, app/bootstrap.php, assets/js/app.js and assets/css/app.css together. The phone review provides visible markup tools and Proof / Comments / Decide navigation. Failed posts retain the current draft and recording; replies return to their saved location. No schema migration is needed. Native build 30007 adds the corrected signed-in toolbar and Android microphone consent/permission.
Keep HTTPS and microphone=(self) enabled. The media-src policy includes self and blob: so local voice previews can play without opening remote media origins. Post-recording transcription needs an administrator-configured provider key; test recording, preview playback and transcription separately. Live recognition is browser-dependent. Unposted audio stays only in the current page, not durable offline storage. Do not claim transcription readiness while its provider is unconfigured.
Push configuration and verification
Custom-server connections support the authenticated in-app activity inbox. This release's remote push integration is for ProofBetter Cloud only: its APNs/FCM tokens and private keys are not shared with self-hosted operators, and Cloud alerts are disabled while a custom server is selected. A separately branded remote-push distribution needs its own coordinated identity, signing, credentials and server integration. Local notification tests do not prove remote delivery. Keep signing and push keys outside public packages and webroots.
Updates and recovery
Web changes load on the next workspace reload. Native changes require a new signed app build with an increased platform build number. Preserve the Android upload key and Apple signing materials separately from deployables; back up them privately. Server recovery must include the database, uploads, configuration, and mobile token/outbox tables. Treat device tokens and backups as confidential.
The review-safety update adds report/block moderation and verified account erasure. Administrators should review Safety center promptly and monitor pending erasure file cleanup. Keep current deletion receipts independently of old archives. New migration kits reject stale or missing erasure checkpoints and leave destinations quarantined for operator activation. Stop source writes and workers, reconcile the current receipts and follow the supplied RECOVERY-AND-ERASURE.md before switching traffic. Old downloaded installers cannot be retroactively revoked and must not be used for activation. Source loss requires isolated, manually verified recovery; no automatic replay of historical erasures is provided.